What Thailand’s PDPA requires
- Have a lawful basis for processing personal data and, where that basis is consent, request it explicitly, in writing or electronically.
- Tell people, before or when you collect their data, the purpose, what you collect, how long you keep it, who may receive it and their rights.
- Allow data subjects to access, correct, delete and port their data.
- Appoint a Data Protection Officer for certain categories of processing.
- Notify the PDPC Office of a personal data breach without delay, and within 72 hours where feasible, unless it is unlikely to put people at risk. Tell affected people without delay when the risk is high.
- Sign data processing agreements with vendors that handle personal data.
What the banner does here
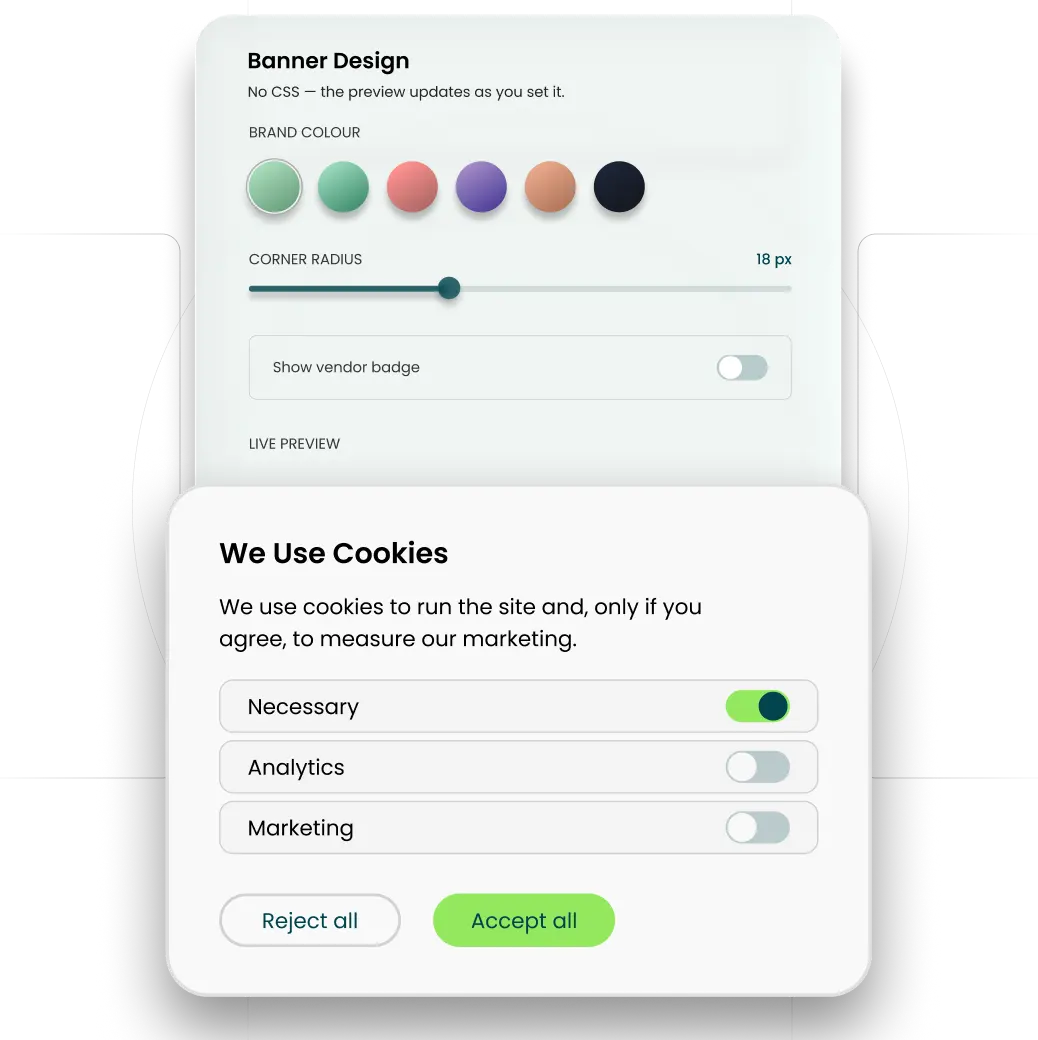
The same opt-in mode as in the EU and UK: non-essential cookies are blocked until the visitor chooses, with Reject all beside Accept all at the same size, and no pre-ticked boxes.
How GrantCookie covers it
- Scheduled scans. The scanner finds the cookies and trackers your site sets, sorts them into categories and re-checks on every scheduled scan, so the banner asks about what is really there.
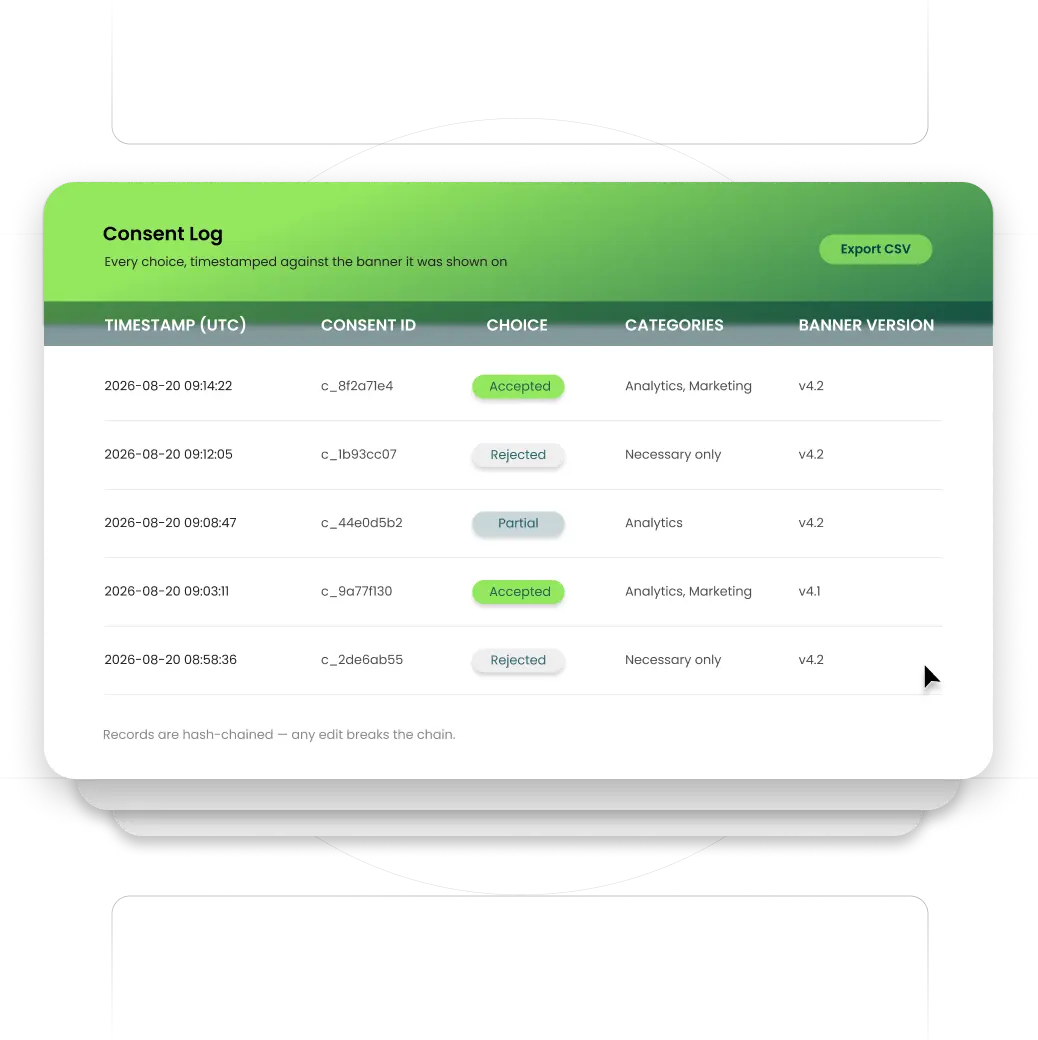
- Provable records. Every choice is timestamped and stored with the banner version the visitor saw. Paid plans include consent log export.
- Withdrawing consent. A re-open control stays on every page, so visitors can withdraw or change their choice at any time.
This page is general guidance. It is not legal advice. Check your specific obligations with a qualified adviser.